Runtime Security for AI Agents: Monitoring What Agents Actually Do
Preventive controls for AI agents will never be perfect, because prompt injection has no complete fix. Runtime security fills the gap: captu…
30 articles tagged AI Security.

Preventive controls for AI agents will never be perfect, because prompt injection has no complete fix. Runtime security fills the gap: captu…

AI systems can now find real, exploitable bugs in mature code, and they are being pointed at everything. That is good news for software qual…

AI agents act on behalf of people, teams and other agents, which makes them non-human identities with an unusual twist: delegated, dynamic a…

MCP has become the standard way AI applications reach enterprise systems, and that makes the MCP layer a security boundary in its own right,…

A tester's view of agentic systems. We break the agent attack surface into four areas (identity, tools, memory and autonomy), describe the a…

A year ago, most AI agents were pilots. Now they run inside ticketing systems, CI pipelines, SOCs and customer service, often with more acce…

Red teaming used to be something a security team did to a finished system. For AI agents, it has to start with the developers who build them…

For two years, 'AI-powered attacks' mostly meant better phishing emails. This summer, public reports showed criminals using agentic AI tools…

A practical hardening guide for security teams responsible for MCP deployments: how to assess MCP servers, configure clients, apply the prot…

The Model Context Protocol has become the standard way to connect AI assistants to tools and data in barely six months. Security researchers…
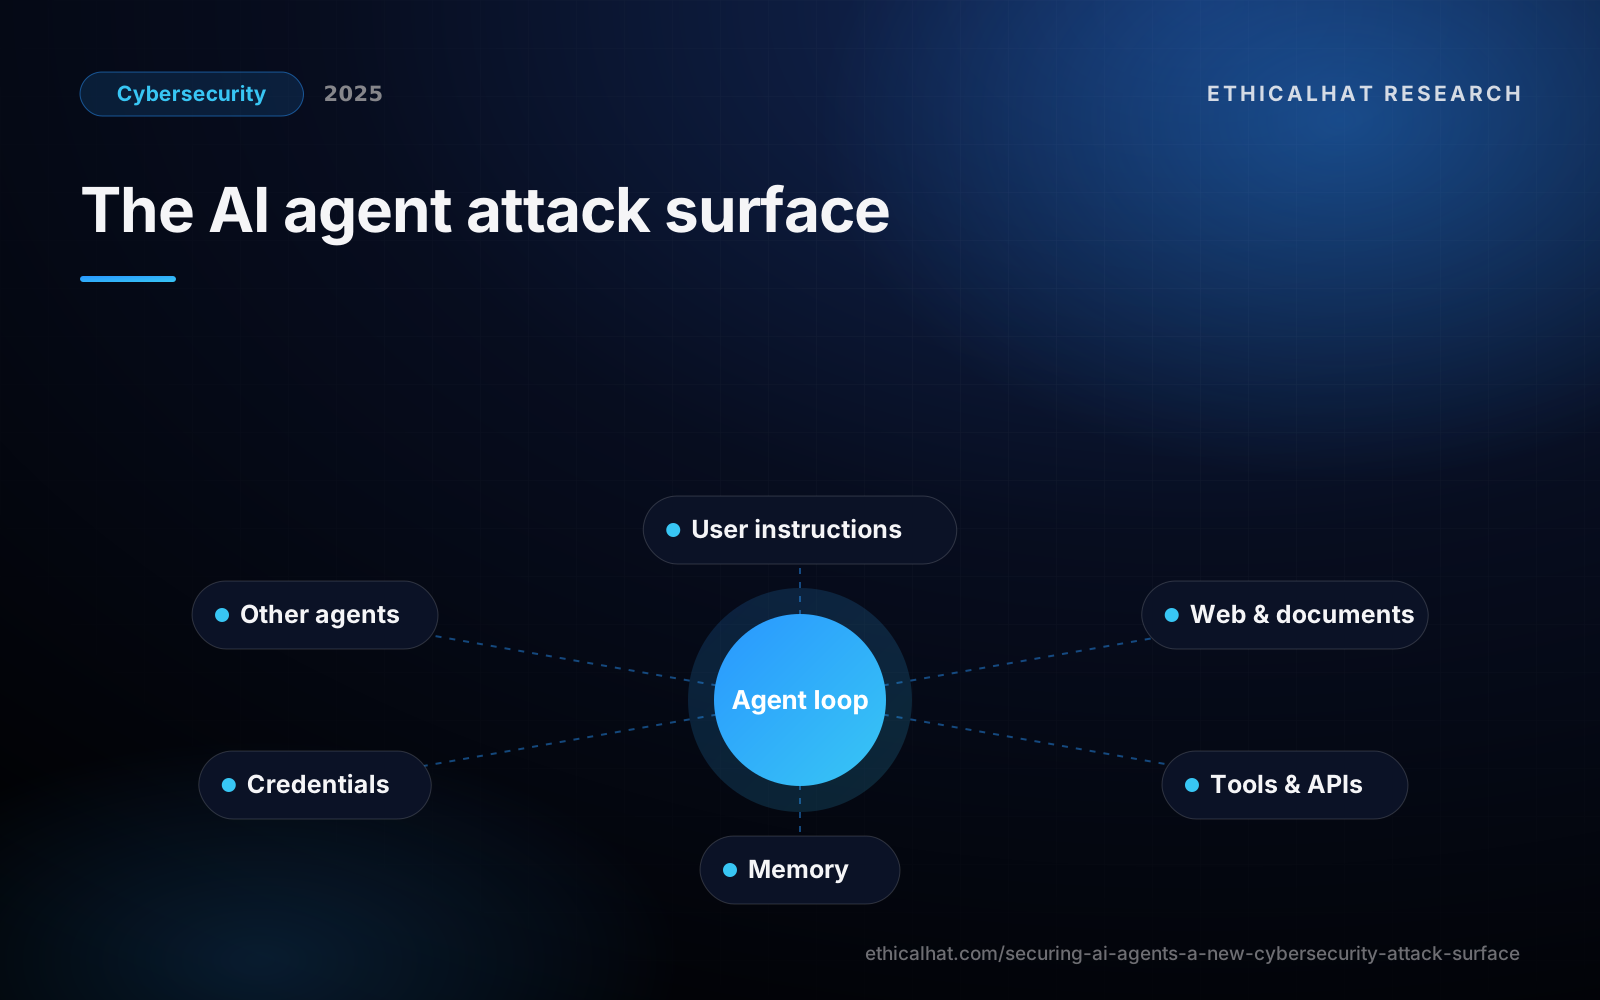
AI agents that browse, write code and operate software on a user's behalf moved from demos to products in the last few months. They combine…
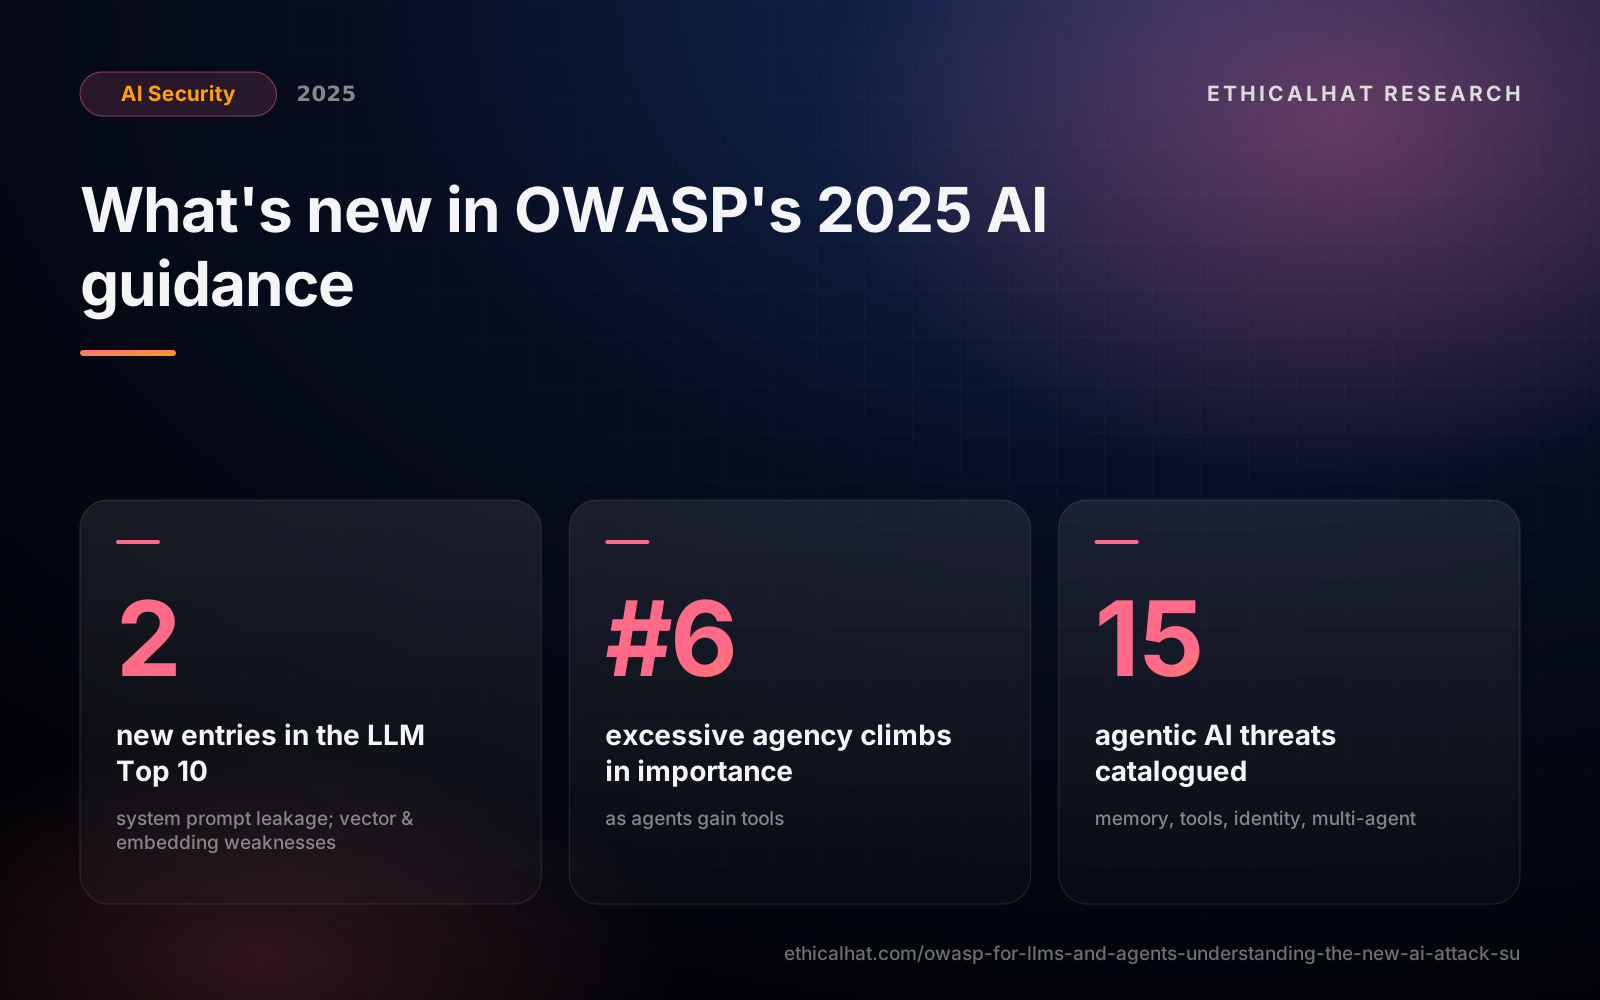
OWASP's GenAI Security Project has published a refreshed 2025 Top 10 for LLM Applications and, last month, a dedicated threat taxonomy for a…
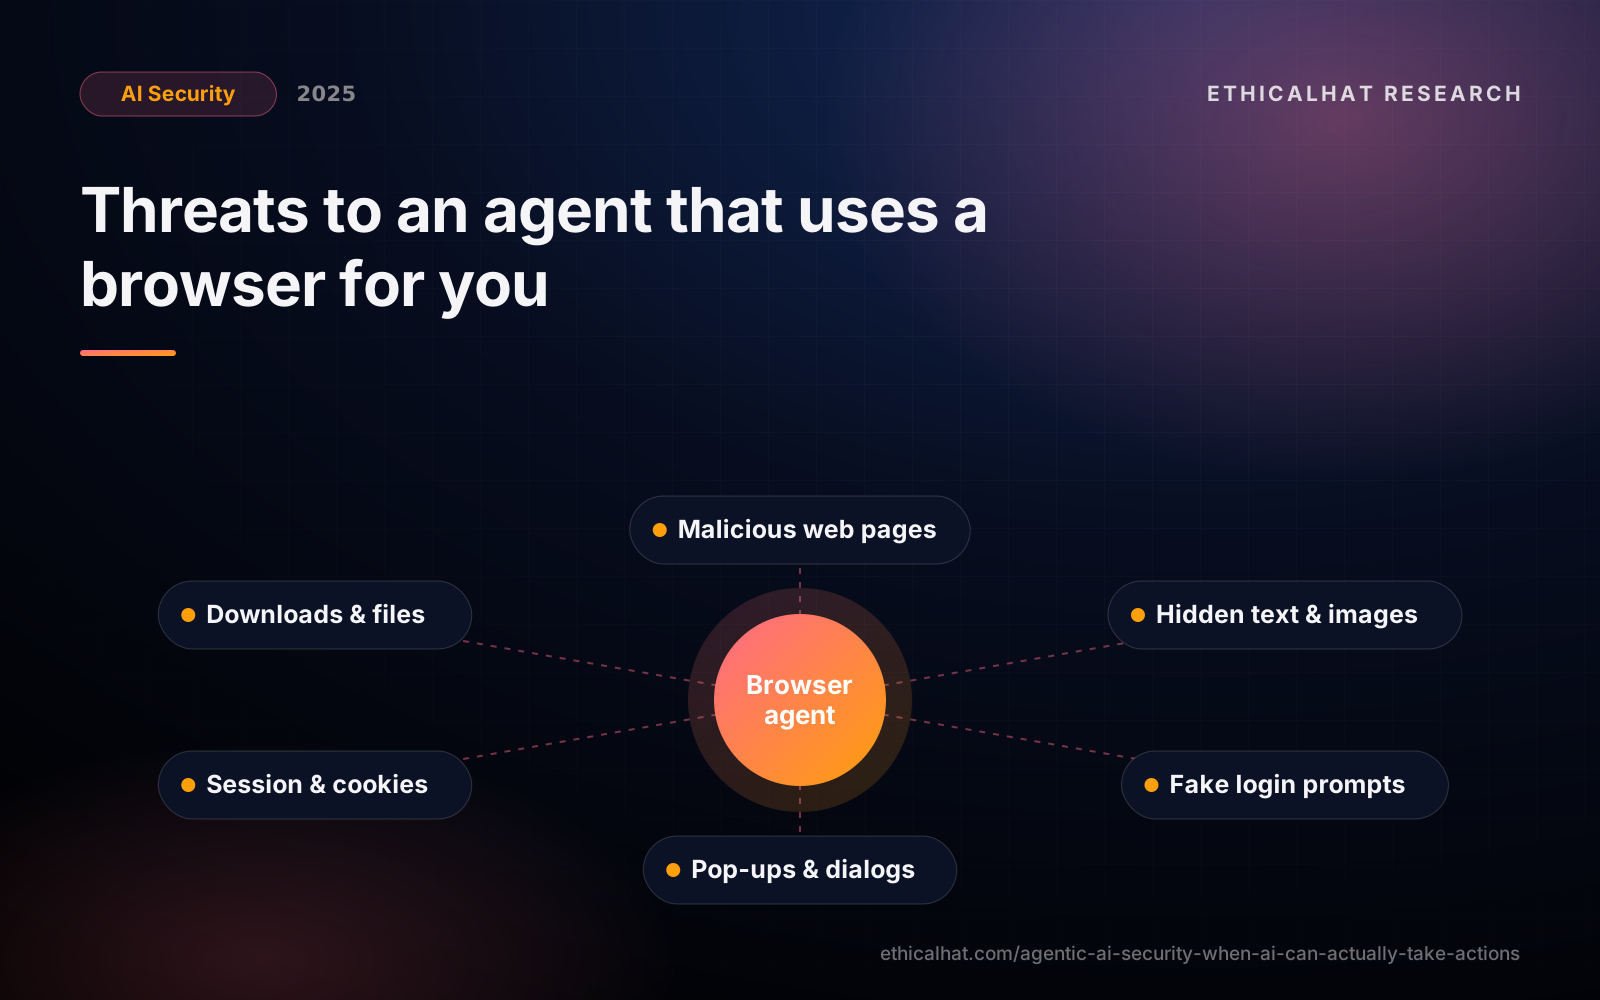
Computer-use and browser agents can now click, type and navigate like a person, in real browsers and desktops, on your behalf. That turns ev…

In November, Google reported an AI agent finding an exploitable bug in SQLite before release, and AI-generated fuzz targets uncovering vulne…

Most organisations now have LLM features in production, and many have never tested them adversarially. This is a practical methodology for r…

Retrieval-augmented generation is how most organisations connect LLMs to their own data, and it introduces risks that are easy to miss: assi…

Last week, researchers reported around a hundred malicious models on Hugging Face that could execute code on anyone who loaded them. AI appl…

Adding a large language model to an application changes its threat model in ways traditional AppSec does not cover. Input becomes instructio…

Thousands of hackers spent DEF CON trying to break AI models, the White House has secured commitments from AI companies to red-team their sy…

OWASP published its first Top 10 for Large Language Model Applications on 1 August. Meanwhile, researchers have shown automated jailbreaks t…

Within days of launch, users persuaded Bing Chat to reveal its hidden instructions, and researchers showed that web pages can silently take…

Within days of ChatGPT's release, security researchers were using it to explain code, draft detection rules and summarise threat reports, an…

Large language models can now write fluent, personalised emails in seconds, and researchers have shown AI-written spear-phishing can outperf…

GitHub Copilot became generally available in June, and code-generating models are now part of everyday development. That has consequences fo…

Criminals have used AI-cloned voices to impersonate executives and authorise large transfers, and the FBI has warned that synthetic media wi…

SolarWinds showed how a patient attacker using legitimate credentials and tools can slip past rule-based detection for months. Behavioural a…

As security products rely more on machine learning, attackers are learning to target the models themselves. Tiny, carefully chosen changes c…

AI promises to help overwhelmed security teams, but it brings problems of its own: alert floods, models that learn the wrong lessons from bi…

Signature-based antivirus has been declared dead many times, and ML-based 'next-generation' endpoint protection has been sold as its replace…

Almost every security product now claims to use AI. Behind the marketing, machine learning has genuinely changed how threats are detected, f…