Policy-as-Code for AI Developers and Autonomous Software Agents
When agents write code, open pull requests, change infrastructure and call tools, written policies and prompts are not enough. Rules have to…
50 articles tagged Application Security.

When agents write code, open pull requests, change infrastructure and call tools, written policies and prompts are not enough. Rules have to…

In an agentic SDLC, AI agents take on work at every stage: specifying, coding, testing, reviewing, releasing and operating. This article des…

Coding agents run commands, read files and make network calls on developer machines and CI runners. Preventive controls reduce the risk, but…

Coding agents run shell commands, read files, use Git and sometimes reach cloud consoles, often on developers' own machines with their crede…

Agents now take part in every stage of the delivery pipeline: writing features, fixing findings, triaging failures and preparing releases. T…

Coding agents now run inside CI pipelines: triaging failed builds, fixing flaky tests, reviewing pull requests and responding to issues. The…

This summer delivered a series of warnings for AI-powered development: an agent deleting a production database, a malicious prompt shipped i…

MCP servers are now part of how software gets built: developers connect coding agents to repositories, ticketing, CI, cloud consoles and dat…

A practical hardening guide for security teams responsible for MCP deployments: how to assess MCP servers, configure clients, apply the prot…

AI applications are built from models, datasets, notebooks, training pipelines, ML frameworks and serving infrastructure, each with its own…
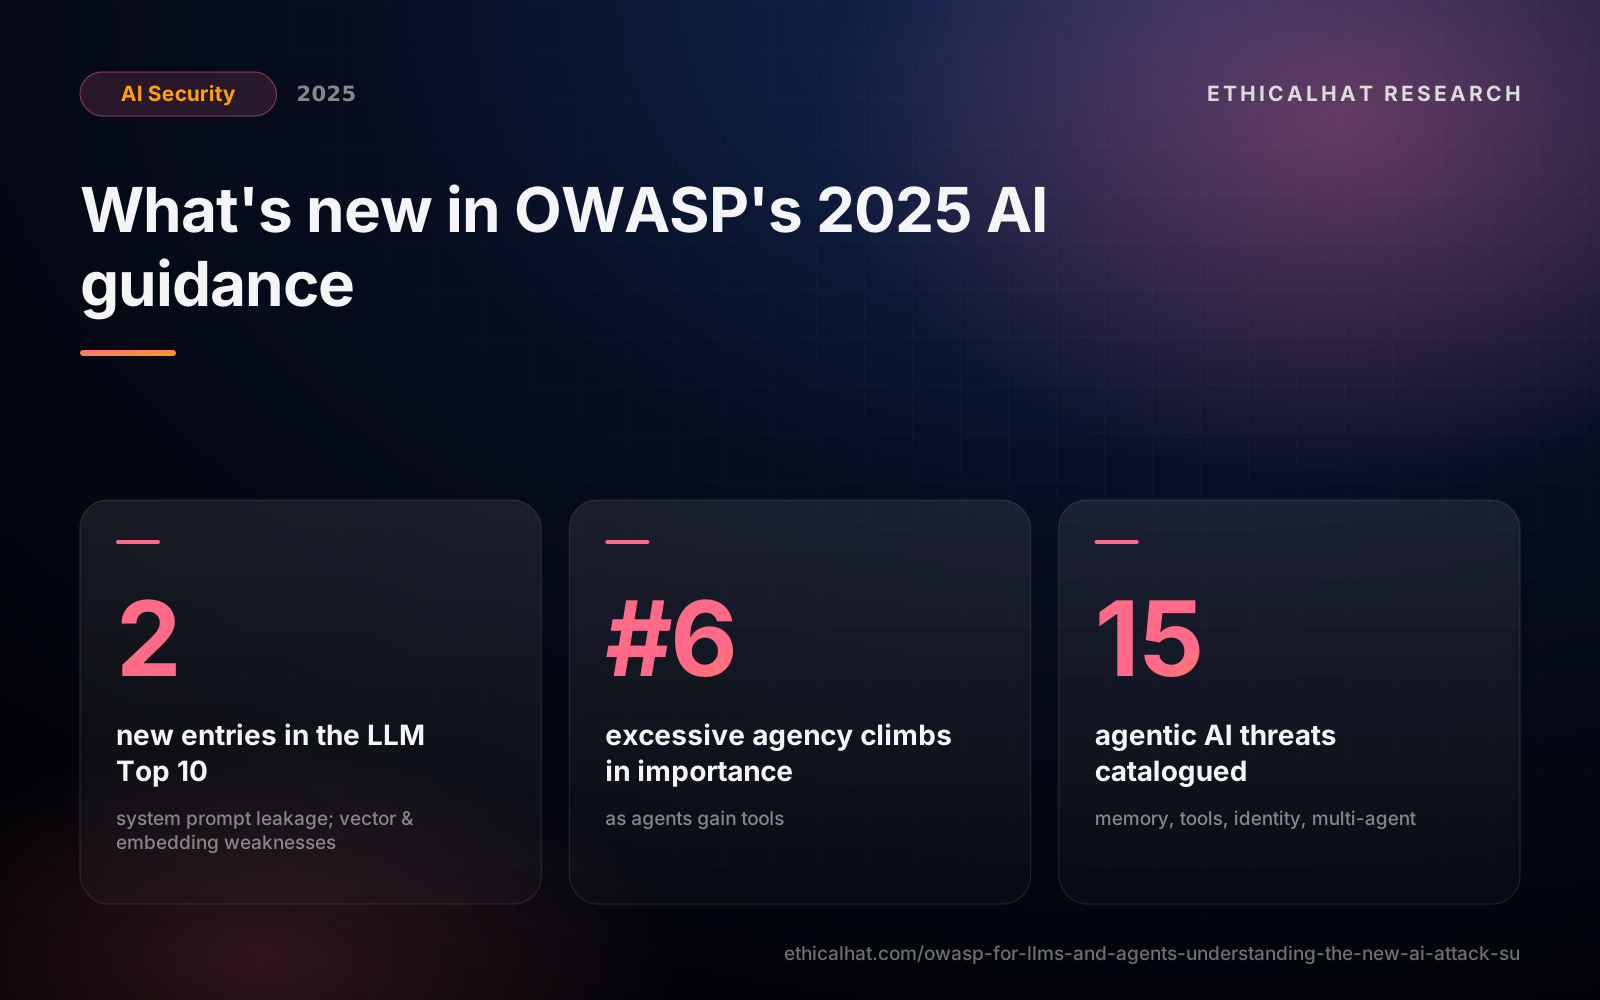
OWASP's GenAI Security Project has published a refreshed 2025 Top 10 for LLM Applications and, last month, a dedicated threat taxonomy for a…

When an AI assistant writes a vulnerability and a developer merges it, who is responsible: the developer, the reviewer, the organisation or…

In November, Google reported an AI agent finding an exploitable bug in SQLite before release, and AI-generated fuzz targets uncovering vulne…

Google has said more than a quarter of its new code is now AI-generated, then reviewed and accepted by engineers. As AI writes more code eve…

Most organisations now have LLM features in production, and many have never tested them adversarially. This is a practical methodology for r…

AI is arriving in application security tooling: automatic fix suggestions for scanner findings, LLM-assisted code review, AI-generated secur…

Retrieval-augmented generation is how most organisations connect LLMs to their own data, and it introduces risks that are easy to miss: assi…

The xz Utils backdoor came within weeks of shipping in major Linux distributions after a two-year social engineering campaign against an ope…

Last week, researchers reported around a hundred malicious models on Hugging Face that could execute code on anyone who loaded them. AI appl…

Adding scanners to one pipeline is easy. Running application security across hundreds of repositories and dozens of teams is not: findings p…

AI red teaming started as something frontier model labs did before releases. With October's US Executive Order on AI and a year of LLM featu…

AI assistants make developers faster, and they also introduce problems that do not show up immediately: insecure patterns delivered with con…

CISA's secure-by-design guidance, expanded last month with more international partners, asks software makers to treat security as a core bus…

OWASP published its first Top 10 for Large Language Model Applications on 1 August. Meanwhile, researchers have shown automated jailbreaks t…

Last month we looked at the new OWASP API Security Top 10 from a security team's point of view. This guide is for the developers who write t…

LLM applications are moving into production faster than security practices are forming around them. This article sets out engineering princi…

APIs now carry most application traffic, and they expose business logic directly to anyone who can read the documentation or a mobile app's…

CISA and its international partners want software makers, not their customers, to carry the burden of security. Their new Secure by Design g…

Within days of launch, users persuaded Bing Chat to reveal its hidden instructions, and researchers showed that web pages can silently take…

Over the holidays, a dependency-confusion attack hit PyTorch's nightly builds, and in January CircleCI told every customer to rotate their s…

Linux 6.1, released this week, is the first kernel with initial support for Rust. Google says Rust is now a significant share of new native…

Infrastructure as code lets teams create cloud environments from reviewed, versioned files, which means cloud misconfigurations can be caugh…

Developers are building products on GPT-3, Codex and Stable Diffusion at a remarkable pace. These applications introduce security problems t…

GitHub Copilot became generally available in June, and code-generating models are now part of everyday development. That has consequences fo…

Containers make applications portable, and they also package operating systems, dependencies and configuration into every image. This develo…

Teams deploy dozens of times a day, and a security review at the end of the release cycle cannot keep up. DevSecOps puts automated security…

AI code assistants are spreading through development teams during Copilot's extended preview, often before security or legal teams have been…

Last month we covered SBOM standards and policy. This article is for developers and build engineers: how to generate accurate SBOMs from rea…

Log4Shell showed that most organisations cannot say what is inside the software they run. A software bill of materials is the fix the US gov…

Eleven days after CVE-2021-44228 went public, most organisations are still answering a simple question: where do we run Log4j? Here is what…

2021 has been the year of software supply-chain attacks, from Codecov to hijacked npm packages last month. Machine learning teams face those…

The OWASP Top 10 was updated last month for the first time since 2017, and broken access control is now the number one risk. This practical…

The Codecov breach disclosed last month showed how a single tampered script could quietly collect the credentials stored in thousands of cus…

Two weeks ago, a researcher showed he could run code inside Apple, Microsoft, PayPal and dozens of other companies simply by publishing pack…

The SolarWinds compromise disclosed this month shows that attackers can turn a vendor's own build process into a distribution channel for ma…

Machine learning projects are built on a deep stack of open-source frameworks, Python packages, pre-trained models and public datasets, ofte…

Testing and bug-finding consume a large share of engineering time, and machine learning is starting to help: predicting which tests to run,…

Application security teams are increasingly asked to review systems with machine learning at their core. Some of their existing knowledge tr…

'Shift left' means finding and fixing security issues earlier in development, where they are cheaper and faster to fix. That only works if d…
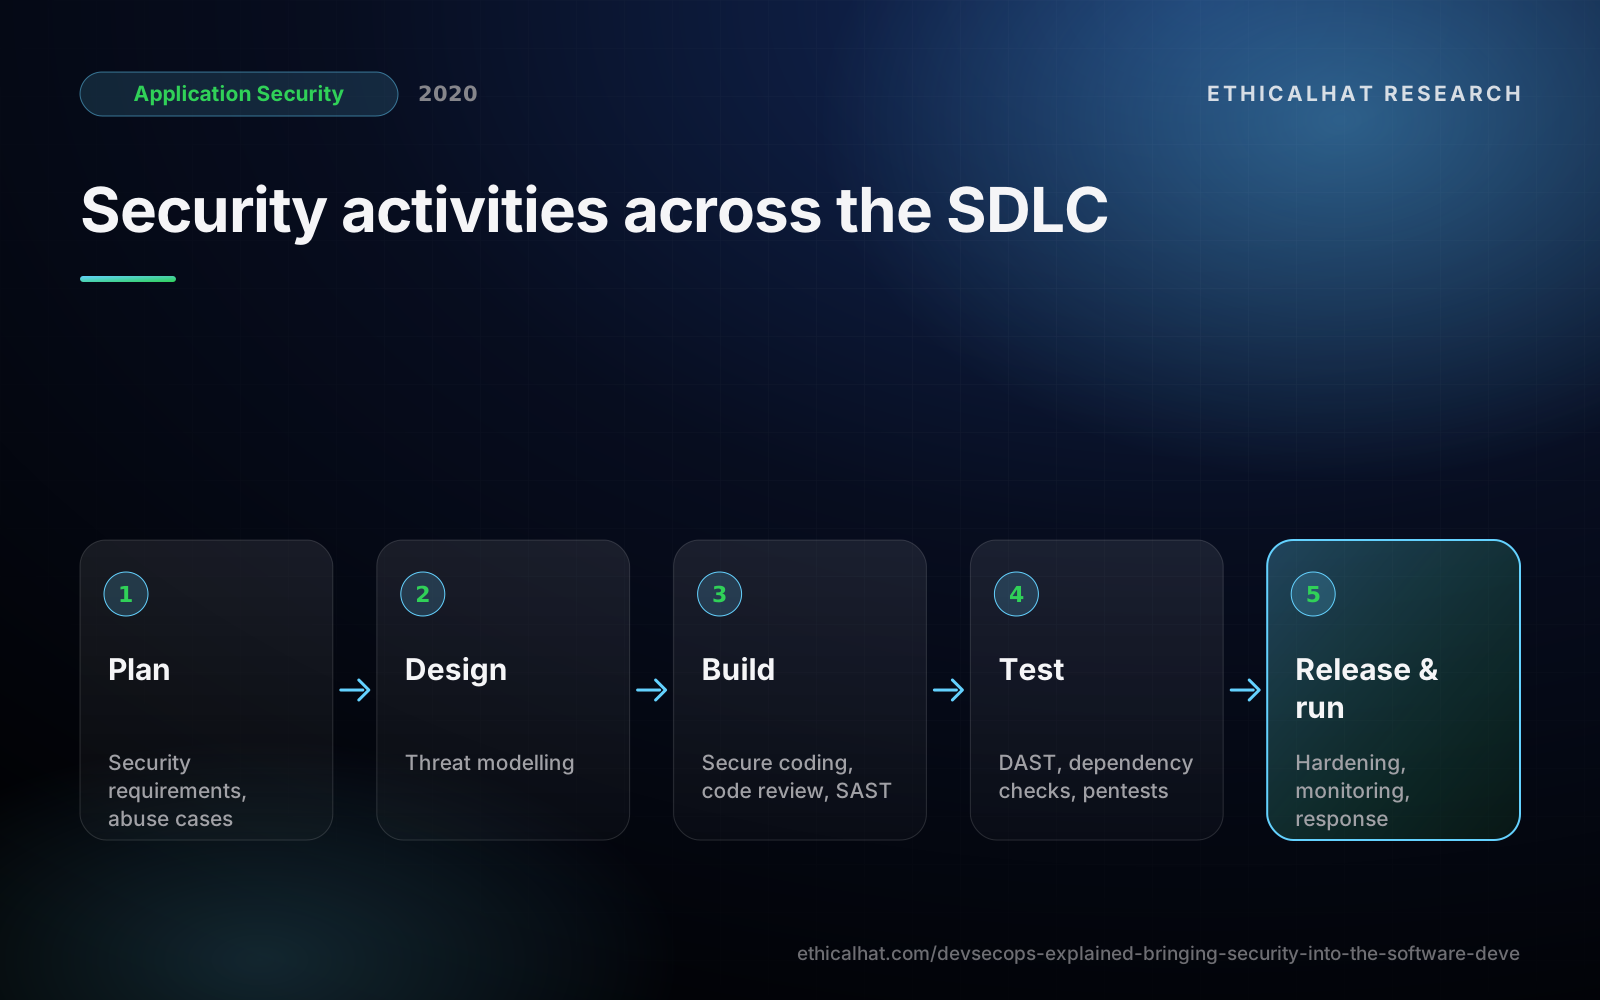
DevOps made software delivery continuous; DevSecOps makes security continuous too. Beyond the buzzword, it is a set of practices that put se…